
Beyond the Alert: Making Cyber Defence Work for the Business
A threat has been detected. The business still has to decide what it means, which services are at risk and what happens next?
For organisations across Australia with multiple security tools and stretched internal teams, that can be where the difficulty begins. Technology produces information but the business requires a coordinated response.
“Many organisations have invested in security technology but still struggle to turn it into coordinated action,” observed Kevin O’Sullivan, Cyber Security Practice Lead at OneStep Group.
“Fragmented tools, limited visibility and stretched teams make it difficult to understand exposure, prioritise threats and respond consistently around-the-clock.”
An organisation can invest in detection and still struggle with prioritisation. It can receive alerts without having the people available to investigate them, or identify a weakness without a clear pathway to address it across the wider technology environment.
O’Sullivan’s concern is the ability to bring those activities together consistently, within the resources available.
“AI adds urgency, but the fundamentals still matter: knowing which services are critical, strengthening controls and being ready to respond,” he outlined. “The challenge is connecting technology, people and business priorities into a security capability that organisations can sustain.”
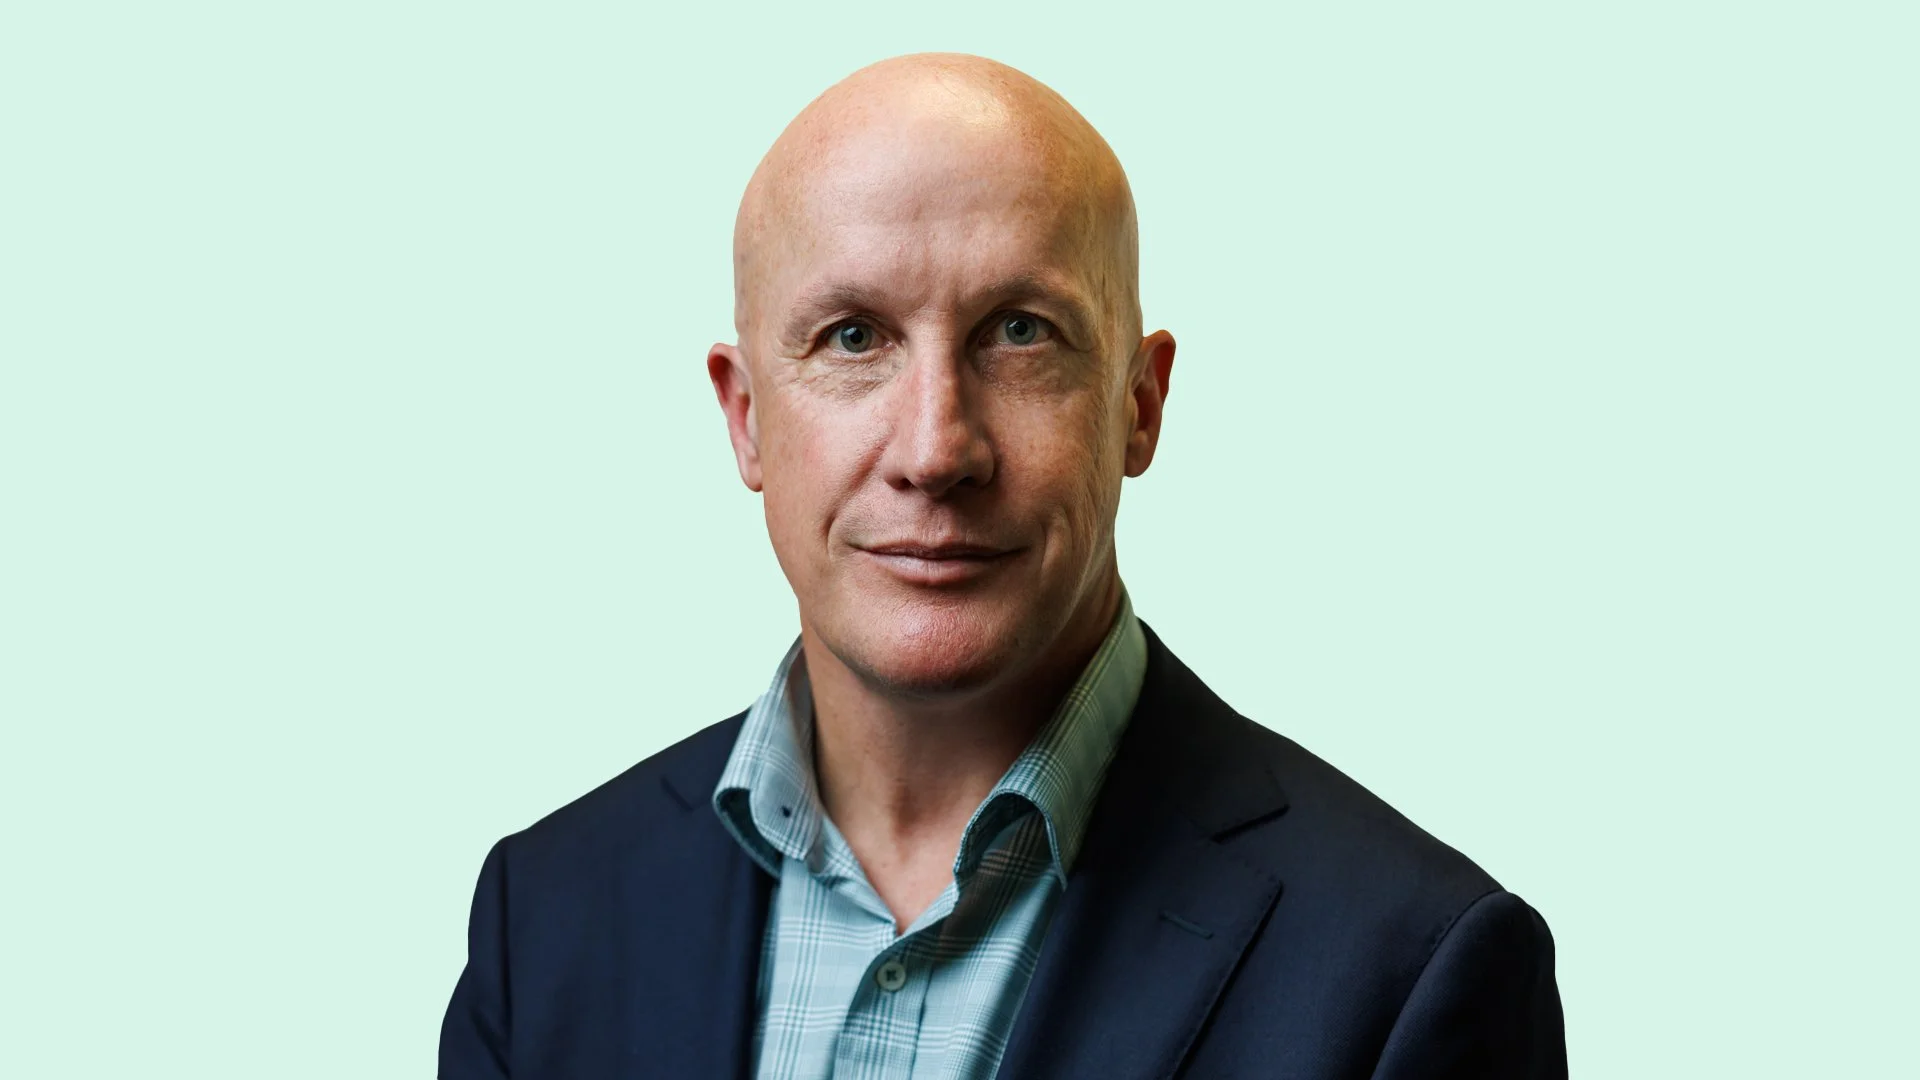
Kevin O’Sullivan – Cyber Security Practice Lead, OneStep Group
That challenge provides the context for OneStep Group’s partnership with Sophos – Managed Detection and Response (MDR) forms part of the approach, alongside advisory, engineering and managed security services.
For businesses, the value will depend on how effectively those capabilities translate into protection they can operate, improve and explain to the business.
Ownership within clear responsibilities
For O’Sullivan, market expectations are moving towards a closer relationship between security operations and business needs.
“Customers want a partner who understands their business, takes ownership within clear responsibilities and helps them improve, not simply sends more alerts,” he said. “They want stronger protection while making better use of existing investments and managing cost.”
The phrase “within clear responsibilities” carries notable weight.
Bringing in a managed security service provider (MSSP) introduces another party into decisions that can affect business operations. Businesses must therefore understand who investigates, who acts and how their internal teams participate.
Those arrangements matter when a threat requires an immediate response. They also matter afterwards, when findings need to become changes to controls, infrastructure or working practices.
An MSSP’s understanding of the business helps place those decisions in context: the services the organisation depends on, the capabilities of its internal team and the constraints influencing investment.
For OneStep Group, that means allowing for different customer circumstances.
“Diversity is central to our strategy: diverse expertise and perspectives, a broader partner ecosystem and meaningful customer choice,” O’Sullivan added.
“That means adapting our services, delivery arrangements and commercial models to each customer’s risk, internal capability and budget, with a practical pathway to mature over time.”
Businesses seeking stronger protection must still make decisions about affordability, implementation effort and the division of work between internal and external teams.
For example, a service that demands more change than the organisation can absorb will be difficult to sustain. O’Sullivan’s emphasis on a pathway to maturity recognises that security improvement must fit the organisation’s ability to carry it through.
The capability behind the response
Maintaining security operations around-the-clock is one of the primary pressures the partnership seeks to address.
The aim is to tackle a dual roadblock – the pace of threats and the challenge of sustaining the necessary expertise.
“As cyber threats become more sophisticated and AI drives faster attacks, organisations are finding it harder to keep pace and deliver their own SOC solutions; security skills shortages compound this and continue to be roadblocks in maintaining a 24x7 in-house security operations team,” stated Aaron Jacobs, Pre-sales Engineer, Global Sales Engineering at Sophos.
“Sophos MDR provides organisations with around-the-clock threat detection, threat hunting, and incident response expertise without the cost and complexity of building those capabilities themselves.”
The demands of an internal security operations centre (SOC) extend across coverage, investigation and response, with expertise available when an incident occurs.
For businesses whose IT teams already carry broad operational responsibilities, access to that capability can change the work they are able to undertake internally. The service still needs to connect with their environment and operating arrangements.
“Sophos MDR’s threat analysts combine decades of experience and knowledge into a service built upon an AI Native defence system which can dramatically augment any internal IT team,” Jacobs added.
According to O’Sullivan, the strategic partnership centres on the broader Sophos Fusion system with MDR forming part of a “connected approach” to cyber defence.
“We align our advisory, engineering and managed security services with that system, bringing together prevention, detection, response and continuous improvement around the customer’s business priorities,” he explained.
Sophos supplies security operations capability, while OneStep Group brings the services and expertise to connect it with the broader requirements of the business.
Detection is one stage in a sequence of decisions and actions; its business value depends on how effectively the organisation can move through the rest.
What happens after detection?
Jacobs is explicit about the work Sophos MDR undertakes once a threat is identified – this is a solution that goes beyond simply detecting threats.
“Our service is designed to deliver outcomes, not just alerts,” he explained. “When a threat is identified, our experts investigate its scope, determine business impact, and take action to contain or neutralise it.”
Jacobs also highlighted the actions that can follow.
“This can include isolating compromised devices, disrupting attacker activity, providing guided remediation, and supporting recovery efforts,” Jacobs added.
“By combining world class threat intelligence, AI powered security operations, and human expertise, Sophos MDR helps organisations move from detection to response quickly and more confidently.”
Isolating a device, containing attacker activity and supporting recovery brings security operations into direct contact with the customer’s technology environment. The response needs to account for the services being protected and the operational consequences of the actions taken.
OneStep Group’s contribution extends into the improvements that follow those findings.
“We connect security operations with governance, exposure management, incident readiness and secure transformation,” O’Sullivan said.
“Our expertise across the network, data, cloud and infrastructure helps integrate those capabilities into the customer’s environment and turn security insights into practical improvements.”
A security finding can require action across several disciplines. Addressing an issue may involve engineering work, a control change, a governance decision or preparation for a future incident.
O’Sullivan positioned OneStep Group as the partner connecting those activities. Its expertise across the wider IT environment provides a way to carry findings into the work required to strengthen that environment.
Recurring issues should, in turn, inform decisions about what needs to change, where effort should be directed and which investments deserve priority.
Working with the business reality
An organisation considering managed security rarely starts with an empty technology estate, however.
Most businesses have existing investments, internal expertise and delivery arrangements – introducing another capability can raise questions about integration, priorities and the work required from its people.
Hence why O’Sullivan makes flexibility a central part of OneStep Group’s approach.
“Flexibility is fundamental,” he clarified.
“We work with existing technology and internal teams, tailoring service scope, implementation priorities and commercial arrangements to customer requirements.”
Some organisations will have internal expertise that needs additional coverage or specialist support. Others will require a broader contribution across advisory, engineering and managed operations.
The appropriate scope depends on the responsibilities the customer can sustain and the gaps it needs a partner to address.
Jacobs identified OneStep Group’s understanding of the customer as an important part of making that capability effective.
“Sophos delivers the security operations capability, while OneStep Group helps ensure those capabilities are aligned to the customer's broader IT portfolio and strategic needs,” he said.
That alignment influences how capabilities are introduced and how security work fits with other technology priorities.
O’Sullivan applied the same discipline to automation and AI-supported defence.
“Fusion provides a foundation for advancing automation and AI-supported defence, while OneStep Group helps customers adopt those capabilities with clear oversight, measurable value and a realistic pathway to greater resilience,” he outlined.
The conditions attached to adoption – oversight, measurement and a realistic pathway – keep the discussion grounded in the business’ ability to use the capability effectively.
For CIOs and CISOs, the decisions include which activities to automate, how to oversee them and how to establish whether they are improving security operations.
Making improvement visible
The partnership’s stated aims are clearer visibility, more coordinated response and a reduced burden on internal teams. Demonstrating progress requires an agreed basis for assessment.
“Customers should expect clearer visibility of priority threats, more coordinated response and less operational burden on their teams,” O’Sullivan said.
“Over time, the aim is stronger resilience and a more informed basis for security investment. We agree measures upfront and use service reviews to show progress, from detection and response, performance to coverage, recurring issues and control improvements.”
The inclusion of coverage, recurring issues and control improvements broadens the assessment beyond individual incidents. Service reviews can examine whether weaknesses are being addressed and where further work is required.
“For business leaders, we connect those measures to critical services, operational disruption and investment priorities,” O’Sullivan expanded.
That connection gives security reporting a practical purpose: helping the organisation understand the protection of services it depends on and the investment required to strengthen them.
“OneStep Group plays a critical role in the customer security journey as they understand business objectives, operational environments, and risk profiles,” Jacobs summarised.
“Together, Sophos and OneStep Group provide customers with more than a security service. We provide a trusted partnership that helps organisations improve resilience, reduce cyber risk, simplify security operations, and focus on achieving their business goals with confidence.”
In parallel, O’Sullivan’s final assessment also recognises the sustained work behind that ambition.
“We are realistic about what any service can achieve: resilience improves through a sustained partnership, clear responsibilities and continuous improvement,” he concluded.
Talk to OneStep Group about moving from alert-driven security operations towards an intelligence-led, continually improving security capability.
Contact us here